Dariusz Zalewski

- Head of Information Security
- Chief Information Security Officer
- ISO/IEC 27001 Lead Auditor
- ISMS Architect & Auditor
15+ years building, leading and auditing enterprise security programmes across globally distributed organisations. ISO/IEC 27001 Lead Auditor with deep expertise in compliance, risk and zero-trust architecture, driving measurable risk reduction at scale.
- Based in
- Warzymice, PL
- Focus
- InfoSec · CISO
- Status
- Available
- In IT
- since 2008
Languages
- EnglishC2Proficient
- PolishNativeMother tongue
- GermanB2Independent
Strategic leadership with hands-on technical depth.
Results-driven Information Security and IT leader who has built, run and audited enterprise security programmes for globally distributed SaaS and retail organisations, from zero-trust architecture and endpoint security to ISMS governance and vendor risk.
I pair board-level strategy with the engineering credibility to design the controls myself, then prove they work through independent audit.
1.1Normative references
- ISO/IEC 27001:2022
- ISO 22301:2019
- ISO/IEC 42001:2023
- ISO 9001:2015
- ISO/IEC 20000-1:2018
- ISO/IEC 27017
- ISO/IEC 27018
- SOC 2 Type II
- PCI DSS
- NIS2
- GDPR
Lead Auditor across five ISO standards
Certified to design, run and independently audit management systems, from information security and IT service management to business continuity and AI governance. Select any credential to view the certificate.
- 2.1ISO/IEC 27001:2022
Information Security
Lead AuditorCQI & IRCA · ENR-01412750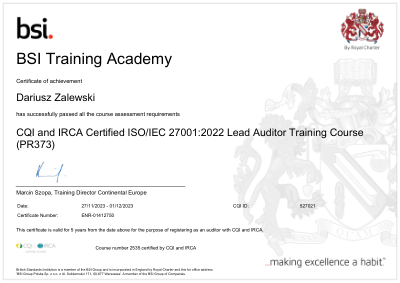 View certificate ↗
- 2.2ISO 22301:2019
Business Continuity
Lead AuditorBSI Group · ENR-01523756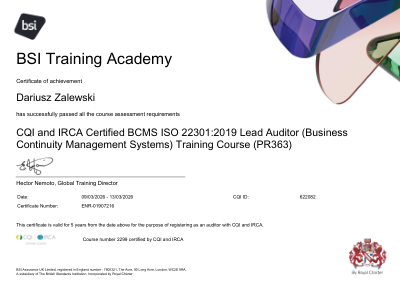 View certificate ↗
- 2.3ISO/IEC 42001:2023
AI Management
Lead AuditorBSI Group · ENR-01522194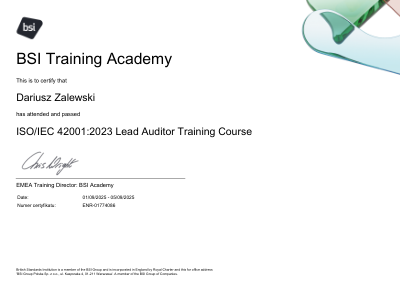 View certificate ↗
- 2.4ISO 9001:2015
Quality Management
Lead AuditorBSI Group · ENR-01675378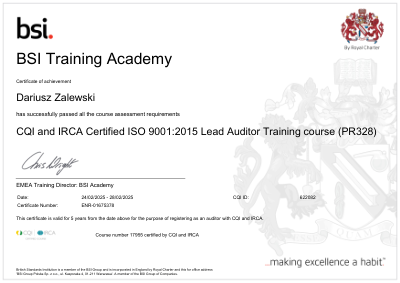 View certificate ↗
- 2.5ISO/IEC 20000-1:2018
IT Service Management
Lead AuditorBSI Group · ENR-01933670 View certificate ↗
Further verified credentials
- 2.6ISO/IEC 27001:2022
Information Security
IRCA Associate AuditorCQI & IRCA · 01/03/2025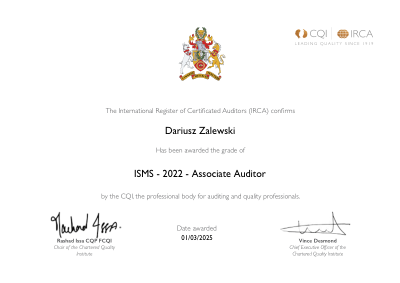 View certificate ↗
- 2.7ISO 22301:2019
Business Continuity
Internal AuditorBSI Group · ENR-01523756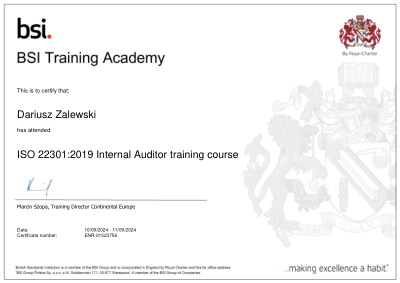 View certificate ↗
- 2.8ISO/IEC 42001:2023
AI Management
Internal AuditorBSI Group · ENR-01563383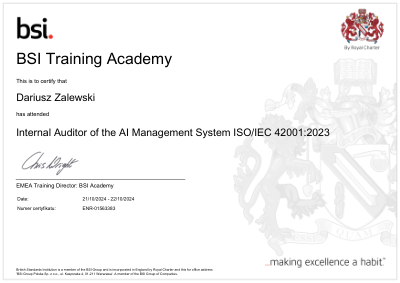 View certificate ↗
- 2.9ISO/IEC 27017 · 27018
Cloud Security & Data Protection
TrainingBSI Group · ENR-02088885 View certificate ↗
- 2.10ISACA
Professional Membership
MemberISACA · 27/05/2024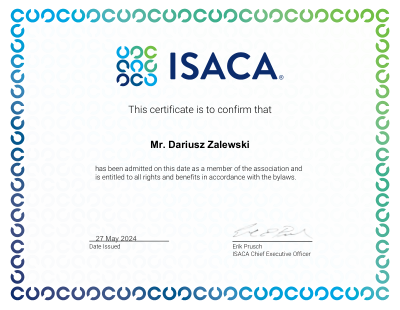 View certificate ↗
2.11Other training
- C)ISSO (Mile2)
- NSE 4 (FortiGate)
- AgilePM® Foundation
- MongoDB Administrator
- NSE 4 · Azure · System Center
Experience
Director of IT & Security
Alokai Inc. (formerly Vue Storefront)
ISMS owner and Compliance Officer for a global SaaS company. Governs full compliance with ISO 27001:2022, SOC 2, PCI-DSS Service Provider Level 2 and NIS2; runs every audit cycle end-to-end and leads the zero-trust, zero-touch MDM programme.
Head of Security & Compliance
KeyShot ApS
Built the ISO 27001 ISMS and SOC 2 programme from the ground up, owned the full vulnerability lifecycle, and served as Data Protection Officer (DPO) for GDPR, embedding security and privacy by design across engineering, legal and product.
VP, Head of IT Operations
Zoovu Limited
Led global TechOps, DevOps and IT Support. Delivered ISO 27001 and SOC 2 certifications from scratch, established business-continuity controls on Fusion Framework, and drove cloud hardening and privilege segregation.
IT Director, Central Europe
Ramirent S.A.
Led IT strategy and transformation for 1,000+ employees across 300+ locations, including security-zone segregation, Azure cloud migration and a group-wide Office 365 / Azure AD rollout.
Group IT Infrastructure Manager / Interim CIO
Change of Scandinavia
Owned infrastructure and security across offices in 11 countries: IT security policies and SOPs, GDPR compliance, complex disaster-recovery solutions and full Azure / Dynamics environments.
IT Systems Administrator / Deputy Infra Manager
Change of Scandinavia · Prime Cargo
Managed Windows Server, AD and Exchange estates and wrote server security standards. Implemented an MS BizTalk EDI solution that cut warehouse picking from 2.5 minutes to 7 seconds per package.
Notable security projects
- 4.1Contained & recovered
RYUK Ransomware Recovery
Incident response · Carlsberg Breweries A/S
Led the full security audit and recovery response following a RYUK ransomware attack. Designed an emergency “Tango Down” containment procedure, hardened Fortinet infrastructure end-to-end, and deployed centralised monitoring with least-privilege network policies.
- 4.22×ISO 27001 + SOC 2
Zero-to-Certified ISMS
ISMS build · Zoovu & Alokai
Designed and implemented complete information security management systems from the ground up across two global SaaS organisations (scoping, risk assessment, control design and audit management), achieving ISO 27001 and SOC 2 certification and managing every surveillance cycle since.
- 4.3400VPN tunnels
Pan-European Secure Network
Infrastructure · Change of Scandinavia A/S
Built an enterprise server room from scratch (12× ESXi hosts, SAN arrays, a VMware HA cluster and FortiGate firewalls) and engineered a 400-tunnel VPN connecting every store and HQ across Europe, then built and led the 17-person infrastructure team to run it.
- 4.47sFrom 2.5 min / pkg
Warehouse EDI Automation
Automation · Prime Cargo A/S
Implemented MS BizTalk integrated with 12 logistics carriers, EDIportal XML, Navision and Consignor, automating the entire warehouse pipeline end-to-end. Picking time per package dropped from 2.5 minutes to 7 seconds.
Operating principle
Security isn't a document set. It's an operating system for the business. I build it to be audited, and run it like it matters.
By the numbers
- 15+Years of experience
- 11Countries operated in
- 300+Sites secured
- 1000+Users supported
Core competencies
5.1Governance & audit
- ISO 27001 ISMS design & audit
- SOC 2 Type I & II
- PCI-DSS & NIS2 compliance
- GDPR & DPO function
5.2Risk & continuity
- Risk management & gap analysis
- Business continuity (ISO 22301)
- Fusion Framework GRC platform
- Vendor & supply-chain risk
5.3Architecture & cloud
- Zero-trust & zero-touch MDM
- Cloud security (Azure, AWS)
- Identity: Okta, AD, Jamf
- Network security: FortiGate
5.4Operations & leadership
- Incident response & recovery
- Security awareness programmes
- Budget & procurement
- Globally distributed teams
5.5 Years on the tools
Security & ISO certifications
- Cybersecurity12 yrs
- ISO 27001 · Lead Auditor11 yrs
- ISO 22301 · Lead Auditor7 yrs
- ISO 42001 · Lead Auditor3 yrs
- Risk management11 yrs
- SOC 25 yrs
Leadership & delivery
- IT management8 yrs
- Leadership8 yrs
- Project management8 yrs
- ITIL processes8 yrs
- IT budget & procurement8 yrs
- Vendor management7 yrs
Infrastructure & cloud
- Networking12 yrs
- Windows Server12 yrs
- Virtualization11 yrs
- Office 365 / Azure7 yrs
- Active Directory12 yrs
- FortiGate firewalls8 yrs
Platforms & data
- MS Exchange11 yrs
- MS SQL Server9 yrs
- MS Dynamics AX / 3655 yrs
- Okta / Jamf5 yrs
- Synology storage10 yrs
- MongoDB4 yrs
Axperts
Compliance & security, delivered.
Founded in 2016, my consultancy has delivered ERP rollouts, IT security audits and ISO certifications for clients across Europe. Today it helps organisations achieve and maintain compliance with international standards, minimising operational and cyber risk through pragmatic, audit-ready implementations.
Visit axperts.pl ↗- A.1ISO 27001Information security implementation & audit
- A.2NIS2Directive readiness & gap remediation
- A.3ISO 22301Business continuity management
- A.4ISO 42001AI management systems & governance
Are you NIS2 & ISO 27001 ready?
Six quick questions for an instant maturity read, no email required.
Do you have a documented, board-approved information security policy (ISMS)?
Do you maintain a risk register with regular risk assessments?
Is multi-factor authentication enforced across all critical systems?
Do you have a tested incident response and business continuity plan?
Do you run security assessments on your key vendors and suppliers?
Have you mapped your obligations under the NIS2 directive?
Open to opportunities
Let's secure what matters.
Seeking a senior Information Security leadership role: Head of InfoSec, CISO or Security & Compliance Lead. Always glad to talk security.